
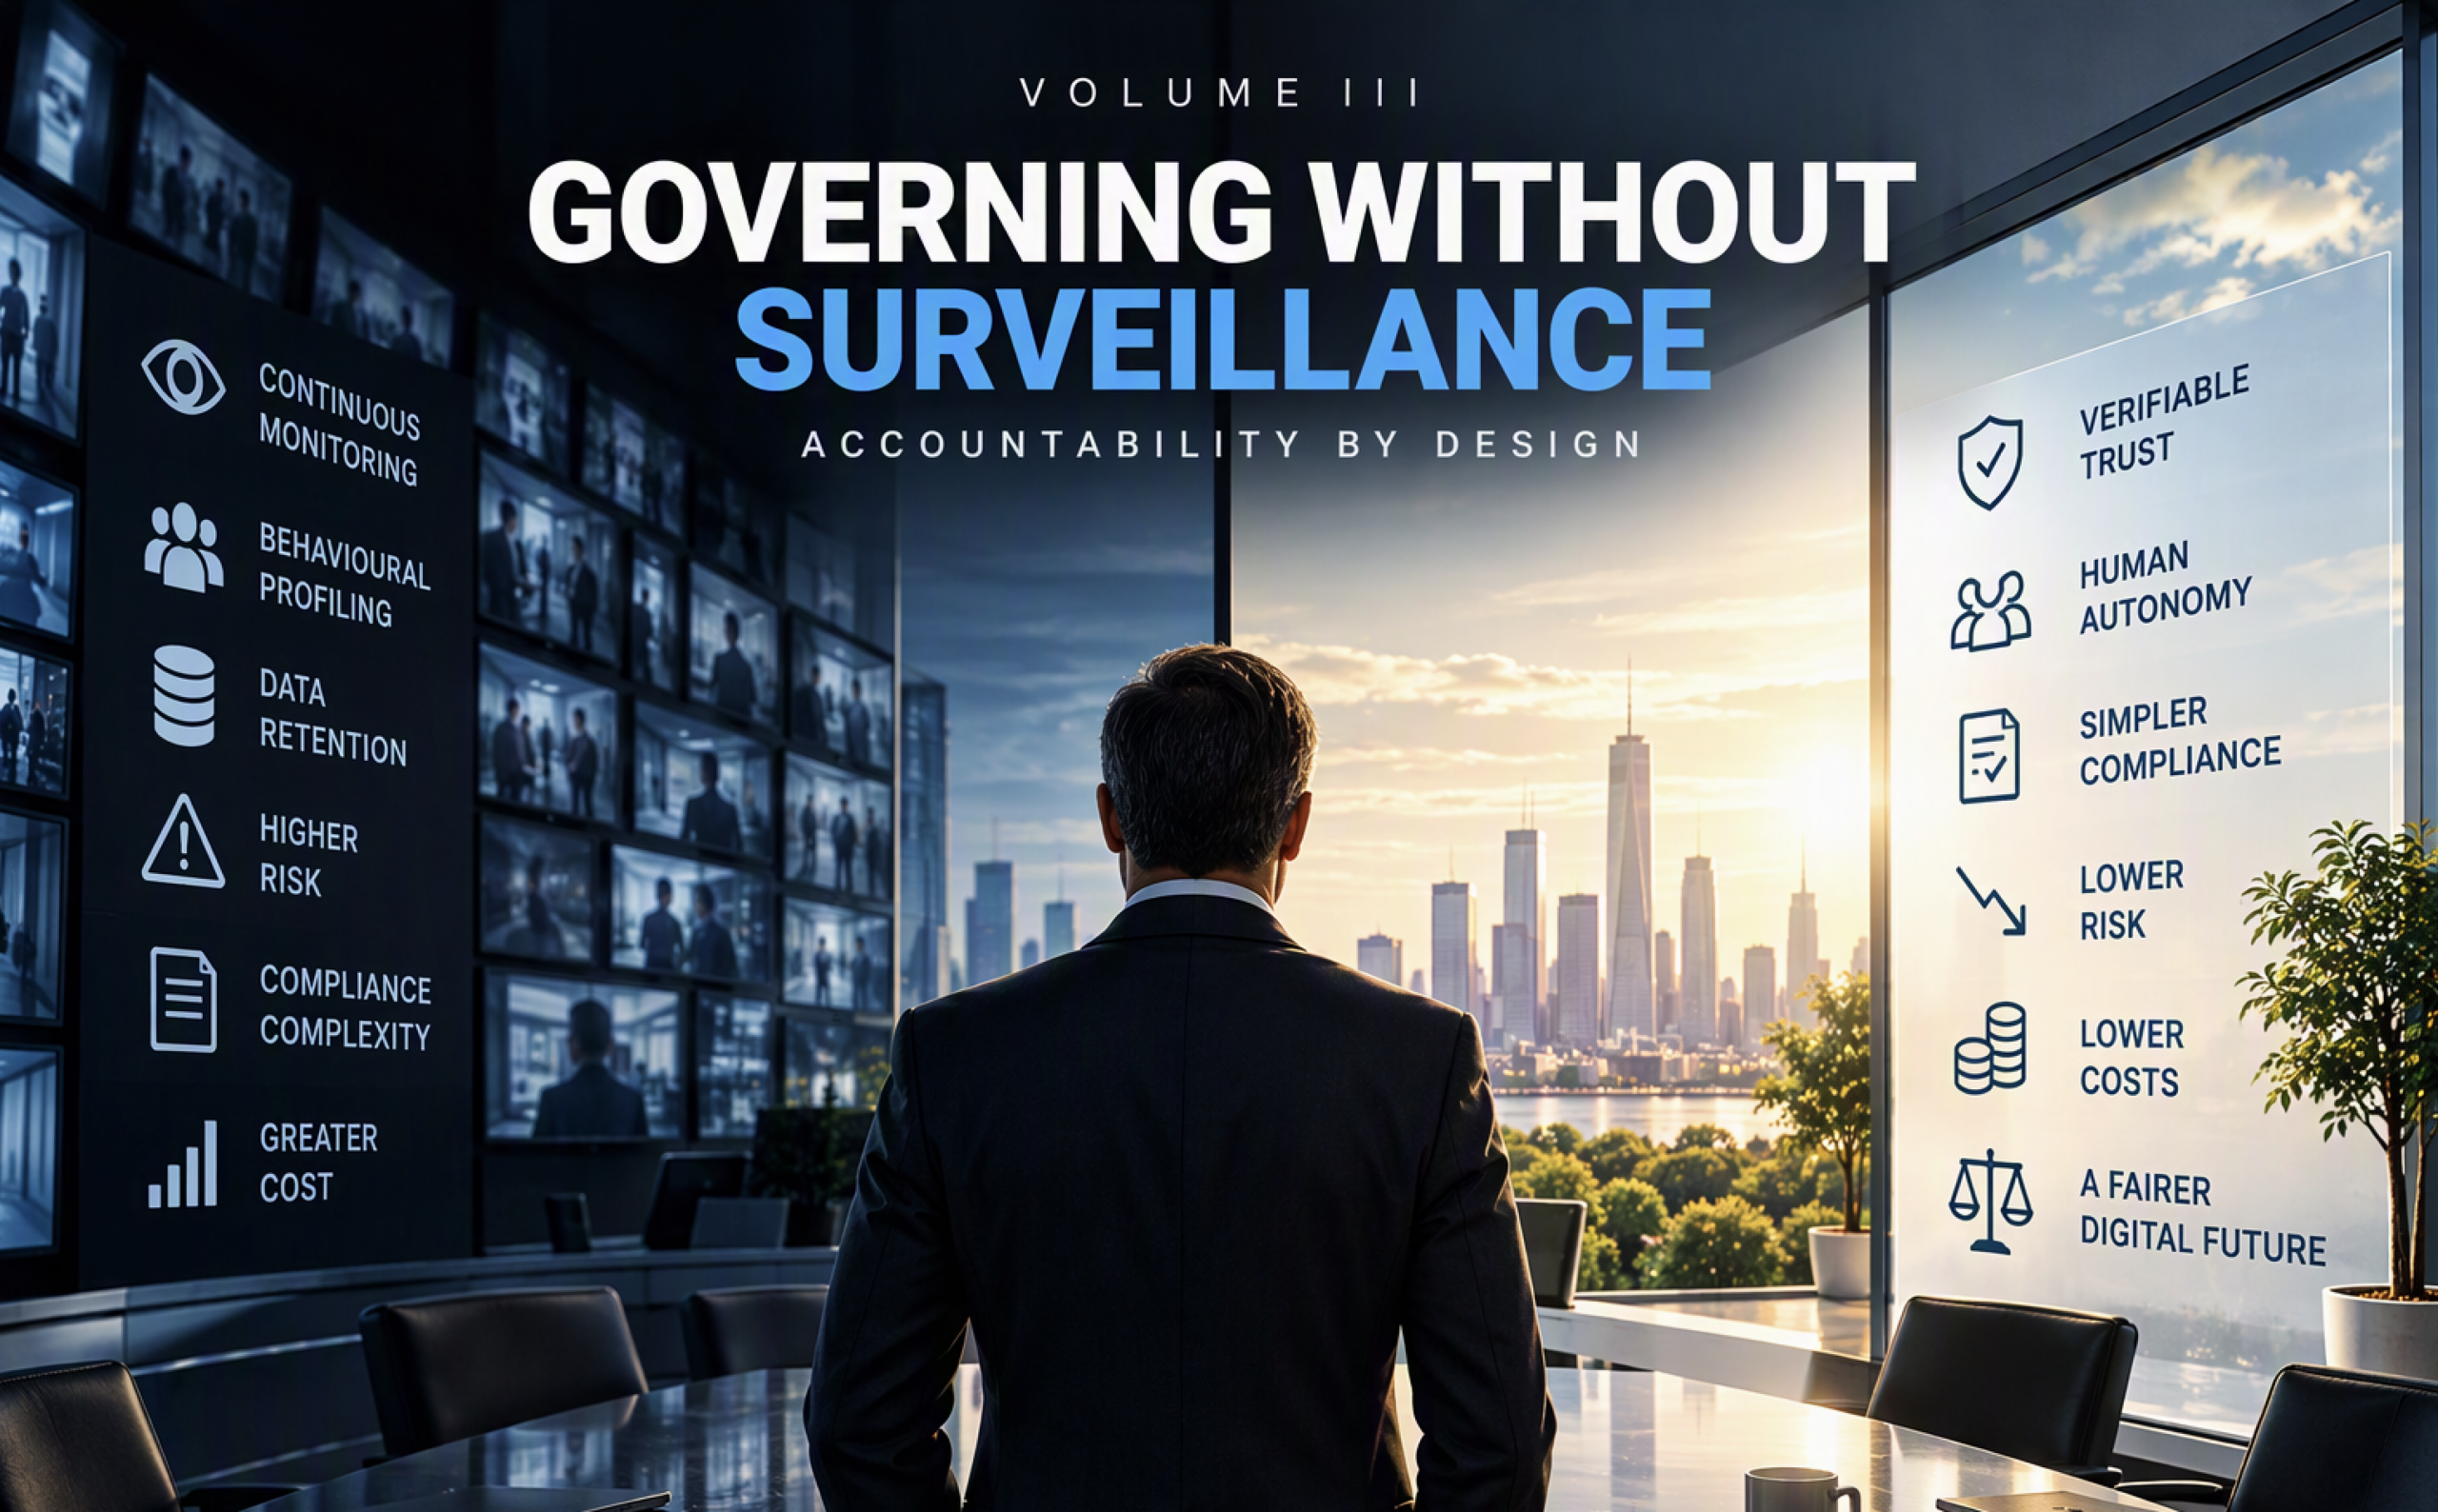
Modern organisations have built much of their governance around visibility.
- We monitor activity.
- We maintain records.
- We analyse behaviour.
- We create audit trails.
We use information to identify risk, demonstrate compliance and provide organisational oversight.
This has created a deeply embedded assumption:
To govern effectively, an organisation needs to see what is happening.
Volume III challenges that assumption.
It asks what happens to enterprise risk, governance, compliance and accountability when observing the individual is no longer the foundation of organisational control.
For leaders considering a greenfield organisation or platform, this creates an opportunity to design governance alongside the architecture from the beginning.
Instead of collecting extensive information and then creating controls around who can access it, how it can be used, and how long it can be retained, leaders can start with a different question:
What evidence does the organisation actually need to establish that something is legitimate, compliant or authorised?
That distinction matters.
Knowing that something is valid does not necessarily require knowing everything about the person or activity behind it.
For existing organisations
The opportunity is different, and potentially more challenging.
Established governance models may depend heavily on visibility, monitoring, data retention and behavioural analysis.
Volume III provides leaders with a framework for questioning those dependencies.
Where is visibility genuinely necessary for accountability?
Where could a right, authority or obligation be validated without exposing everything around it?
And where has monitoring become synonymous with governance simply because existing technologies made monitoring possible?
This is not an argument for removing accountability.
Quite the opposite.
It asks whether accountability can be made stronger by proving what matters without accumulating information that does not.
A different enterprise risk model
Reducing visibility changes the nature of organisational risk.
Information an organisation cannot see cannot become part of a behavioural profile.
Information it does not retain does not require the same forms of protection and governance.
Information that does not accumulate cannot create the same continuity of exposure.
That means provider blindness should not be considered solely as a privacy proposition.
It potentially changes the economics and structure of risk, compliance, governance and institutional responsibility.
The executive challenge therefore becomes:
Can we preserve accountability without building the organisation around observation?
That is the adoption question at the heart of Volume III.
It moves the conversation beyond protecting individuals from unnecessary visibility and asks something larger:
What would enterprise governance look like if trust came from verifiable constraints rather than continuous observation?
Volume III explores that possibility from the perspectives of enterprise risk, law, governance and organisational design.
The underlying ICCA papers are openly shared under a Creative Commons Attribution-ShareAlike 4.0 licence, allowing the principles to be examined, challenged, adapted and developed beyond All Me.
